 Project Management Courses
 Mini Masters Programmes In Management
 Mini Professional Diploma In Management
Short Masters
 Leadership & Professional Development
 Human Resources Training Courses
 Tendering & Contract Management
 Procurement & Warehouses
 Strategic Planning Courses
 Quality Management & 6 Sigma Courses
 Customer Service Courses
 Administrative & Secretariat Courses
 Administrative Skills Courses
 Sales Management Courses
 Education Management Courses
 Retail Management Courses
 Risk Management Courses
 Office Management Courses
 Management Skills Courses
 Logistics and Supply Chain Training Courses
 Hospitality and Tourism Training Courses
 Product Management Training Courses
 Shipping, Maritime and Ports Training Courses
 Facilities Management Training Courses
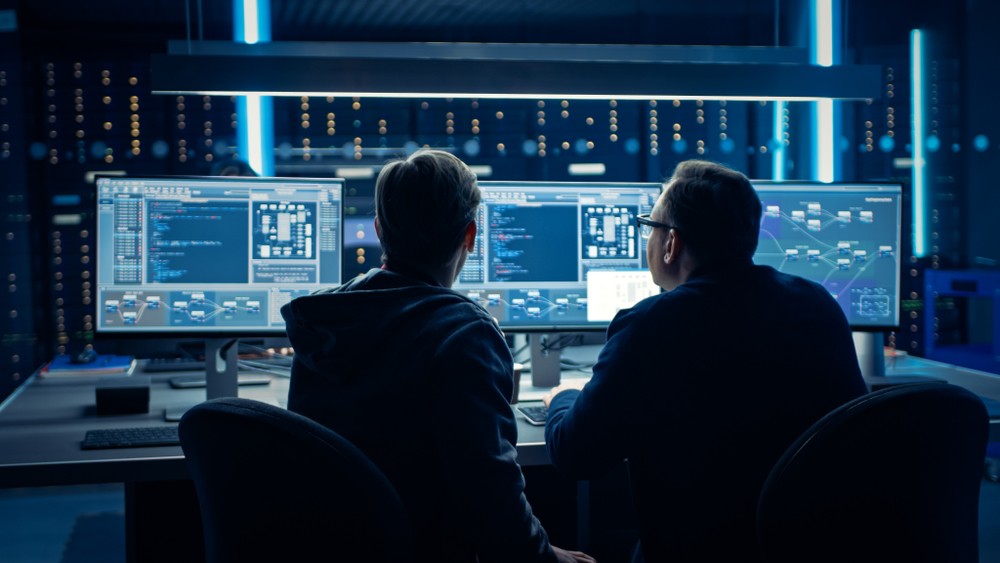
The Security Operations Centre and SIEM Monitoring Training Courses are designed to strengthen organisational capabilities for continuous security monitoring, threat detection, incident analysis and coordinated cyber response. As businesses increasingly depend on interconnected digital environments, security teams require structured processes for identifying suspicious activity, correlating security events and escalating incidents before they develop into significant operational risks.
This corporate-focused programme provides a practical framework for managing Security Operations Centre functions and Security Information and Event Management environments. It addresses the processes organisations use to collect security data, analyse events, identify threats and coordinate appropriate responses across IT infrastructure, endpoints, networks, applications and cloud environments.
The programme focuses on SOC and SIEM operations as an integrated security capability. Participants examine how security logs and event data can be consolidated and analysed to provide meaningful visibility across an organisation. Through effective log correlation, security teams can connect apparently unrelated events and identify patterns that may indicate unauthorised access, malware activity, privilege misuse, data exposure or other security concerns.
Threat detection is a central component of the programme. Participants examine operational approaches for identifying indicators of compromise, unusual behaviour and potential attacks while maintaining appropriate monitoring processes. The programme also addresses alert triage, enabling security personnel to assess alerts according to relevance, severity, business impact and required response.
The course incorporates enterprise SIEM concepts and industry-relevant platforms such as Splunk, with emphasis on operational use rather than product-specific theory. Participants explore how organisations can develop meaningful use cases, establish monitoring requirements and improve the quality of security alerts generated by SIEM environments.
Incident escalation is also addressed as a critical component of SOC operations. Security teams need clearly defined escalation procedures that establish when an alert should move from routine monitoring to investigation, containment or management-level response. The programme therefore considers escalation criteria, communication workflows, incident ownership and coordination between SOC personnel and other business functions.
The British Academy for Training and Development delivers this programme within the Information Technology and Programming Courses category, supporting organisations seeking to strengthen cyber security monitoring, operational resilience and security governance.
The Security Operations Centre and SIEM Monitoring Training Courses aim to develop structured capabilities for managing modern security monitoring operations and responding effectively to detected threats.
By completing the programme, participants will be able to:
Target Audience
The Security Operations Centre and SIEM Monitoring Training Courses are intended for professionals responsible for cyber security operations, information security, technology infrastructure and organisational risk.
The programme is particularly relevant for:
The programme is also suitable for organisations seeking to standardise SOC procedures across multiple teams, improve security visibility or establish more consistent processes for handling security alerts and incidents.
Modules
Module 1: Security Operations Centre Fundamentals
This module examines the organisational role of a Security Operations Centre and its contribution to enterprise cyber security. Participants review SOC responsibilities, operational structures, monitoring functions and the relationship between security analysts, engineers, incident responders and management.
The module considers different SOC operating models and examines how organisations can establish responsibilities for continuous monitoring, investigation, reporting and incident escalation. It also addresses operational procedures that support consistency, accountability and effective coordination.
Module 2: SOC and SIEM Architecture
This module explores the relationship between SOC operations and SIEM technology. Participants examine how security information is collected, processed, stored and analysed to provide centralised visibility across enterprise environments.
Key areas include security event collection, data ingestion, event processing, monitoring dashboards, detection mechanisms and operational workflows. The module focuses on how SIEM capabilities support analysts throughout the security monitoring lifecycle.
Module 3: Security Log Management and Data Sources
Effective SIEM monitoring depends on reliable and relevant security data. This module examines common sources of security logs and events, including network devices, servers, endpoints, applications, authentication systems, cloud services and security controls.
Participants consider log quality, consistency, availability and relevance. The module also addresses the importance of identifying appropriate data sources for specific monitoring requirements and organisational security objectives.
Module 4: Log Correlation and Event Analysis
This module focuses on log correlation as a fundamental capability within SIEM operations. Participants examine how events from different systems can be connected to identify relationships, sequences and behavioural patterns.
The module considers how isolated events may provide limited insight while correlated events can reveal a broader security incident. Participants review approaches for analysing timestamps, user activity, network behaviour, authentication events and system changes to support effective investigation.
Module 5: Threat Detection and Security Monitoring
This module develops operational approaches to threat detection. Participants examine how security teams identify suspicious activity through behavioural indicators, security events, abnormal access patterns and other relevant signals.
The module considers detection requirements across endpoints, networks, applications, identities and cloud environments. It also addresses the importance of maintaining detection capabilities that reflect current organisational risks and evolving attack techniques.
Module 6: Alert Management and Alert Triage
Large-scale monitoring environments can generate substantial numbers of security alerts. This module addresses the operational challenge of assessing, prioritising and managing those alerts.
Participants examine alert triage processes, severity classification, contextual analysis and prioritisation. The module focuses on distinguishing potentially significant security events from routine activity and reducing unnecessary escalation.
Attention is also given to alert fatigue, duplicate notifications and incomplete context. Effective triage enables SOC personnel to focus their resources on events requiring investigation while maintaining appropriate visibility over lower-priority activity.
Module 7: Splunk for SIEM Monitoring Operations
This module introduces Splunk as an enterprise security monitoring platform and examines its role within SIEM operations. Participants explore how security data can be searched, analysed and presented to support monitoring and investigation activities.
The module focuses on operational applications of Splunk, including event analysis, dashboards, security searches, monitoring workflows and investigation support. Participants also consider how organisations can use platform capabilities to develop actionable monitoring processes.
Module 8: SIEM Use Cases and Detection Requirements
Security monitoring is most effective when SIEM capabilities are aligned with defined organisational risks. This module focuses on the development and management of SIEM use cases.
Participants examine how use cases can address scenarios such as suspicious authentication, privilege misuse, unusual network behaviour, malware indicators, unauthorised access and potential data exposure. The module also considers requirements for defining detection logic, relevant data sources, alert conditions and expected analyst responses.
Module 9: Security Investigation and Incident Analysis
This module examines the processes used by SOC personnel when a security alert requires deeper investigation. Participants consider event timelines, user activity, system behaviour, network indicators and related security records.
The focus is on establishing sufficient context to determine whether an alert represents a genuine security incident. Participants also examine documentation requirements and the importance of maintaining consistent investigation records.
Module 10: Incident Escalation and Response Coordination
Incident escalation is essential when security events exceed the responsibilities or authority of frontline monitoring teams. This module examines escalation criteria, incident severity, ownership and communication processes.
Participants consider when an event should be transferred to incident response, infrastructure teams, management or other relevant stakeholders. The module also addresses escalation documentation and communication practices that support coordinated action without unnecessary delays.
Module 11: SOC Performance and Operational Improvement
This module examines methods for reviewing and improving SOC performance. Participants consider operational indicators such as alert volumes, investigation workloads, response processes, detection coverage and escalation activity.
The module focuses on identifying operational weaknesses and opportunities for improvement. Participants examine how organisations can refine monitoring workflows, update use cases, improve data quality and strengthen collaboration between security functions.
Module 12: Enterprise SOC and SIEM Governance
The final module integrates the operational concepts covered throughout the programme into a structured governance framework. Participants examine how SOC and SIEM activities can be aligned with organisational security requirements, internal procedures and risk management objectives.
The module considers operational documentation, access management, monitoring standards, use case governance, escalation procedures and continuous review. The objective is to support sustainable SOC operations capable of adapting to changes in technology, business processes and the cyber threat environment.
The British Academy for Training and Development positions these Security Operations Centre and SIEM Monitoring Training Courses around practical corporate requirements, enabling organisations to develop more structured security monitoring operations, improve threat detection and establish consistent processes for alert triage, investigation and incident escalation.
FAQs
1. What are Security Operations Centre and SIEM Monitoring Training Courses?
These courses focus on the operational management of SOC and SIEM environments, including security monitoring, threat detection, log correlation, alert triage, investigation, SIEM use cases and incident escalation.
2. What is the role of SIEM in a Security Operations Centre?
SIEM technology collects and analyses security events from multiple sources, helping SOC teams centralise security visibility, correlate logs, identify suspicious activity and support security investigations.
3. Does the programme cover Splunk?
Yes. The programme includes a dedicated module covering Splunk for SIEM monitoring operations, including security data analysis, searches, dashboards and monitoring workflows.
4. Why is alert triage important in SOC operations?
Alert triage helps security teams assess and prioritise large volumes of security notifications according to relevance, severity and potential business impact, allowing appropriate resources to be directed towards events requiring investigation.
5. What does incident escalation cover?
Incident escalation covers the procedures used to transfer significant security events from routine monitoring to appropriate incident response, technical teams or management based on defined severity and escalation criteria.
Note / Price varies according to the selected city
Internet of Things Training Program
2026-10-26
2027-01-25
2027-04-26
2027-07-26
 Protocol and & Management
 Diplomacy & International Relations
 Media & Journalism
 Public Relations
 Telecommunication Courses
 Information Technology and Programming Courses
 Graphics & Design Skills Courses
 Programming & Coding Courses
 Cybersecurity and Digital Security
 Environment Municipality management
 Urban Planning and City Building Courses
 Accountancy & Bookkeeping Courses
 Corporate Governance & Anti Corruption Courses
 Investment & Banking Training Courses
 Financial Reporting And Auditing
 Medical Training and Continuing Education
.png) Public Health and Epidemiology in Healthcare
 Healthcare
 Healthcare Policy, Planning, and Advocacy
.png) Medical Quality Improvement and Patient Safety
 Office Management in Healthcare
 Healthcare Risk Management
 Retail Management in Healthcare
.png) AI in Strategic Planning
 AI in Administrative & Secretariat
 AI in Customer Service
 Oil and Gas Training Courses
 Renewable and Clean Energy Training Courses
 Electricity and operation & maintenance
 Health & Safety Training Courses
 Public Health & Hospital Management Courses
 Training Courses in Engineering Maintenance
 Engineering Management
 Construction and Civil Engineering Training Courses
 Operations Readiness and Assurance